Shopping Cart

- Articles
- Cybersecurity
- Anti-Phishing in Saudi Arabia: How KnowBe4 Stops Attacks
Anti-Phishing in Saudi Arabia: How KnowBe4 Stops Attacks
Discover how KnowBe4's anti-phishing solutions help Saudi businesses prevent phishing attacks, reduce human risk, strengthen email security, and improve cybersecurity awareness.
By Blue Edge Team | Published Jul 05, 2026 | Updated Sep 23, 2026 | 5 min read
Quick answer
Phishing attacks are among the most prevalent cyber threats facing Saudi Arabian organizations today. KnowBe4 addresses this threat through automated security awareness training, simulated phishing campaigns, and real-time risk reporting—helping businesses across the Kingdom build a security-first workforce culture.
Phishing does not require sophisticated malware or advanced hacking techniques. A convincing email, a spoofed logo, and a moment of distraction—that is all it takes. For Saudi Arabian enterprises navigating an accelerating digital economy, this reality has become one of the most pressing cybersecurity concerns of the decade.
According to the Saudi Authority for Cybersecurity (NCA), phishing remains one of the top three attack vectors targeting organizations across the Kingdom. As Vision 2030 drives rapid digitization across sectors—from financial services to healthcare and government—the attack surface for social engineering grows alongside it.
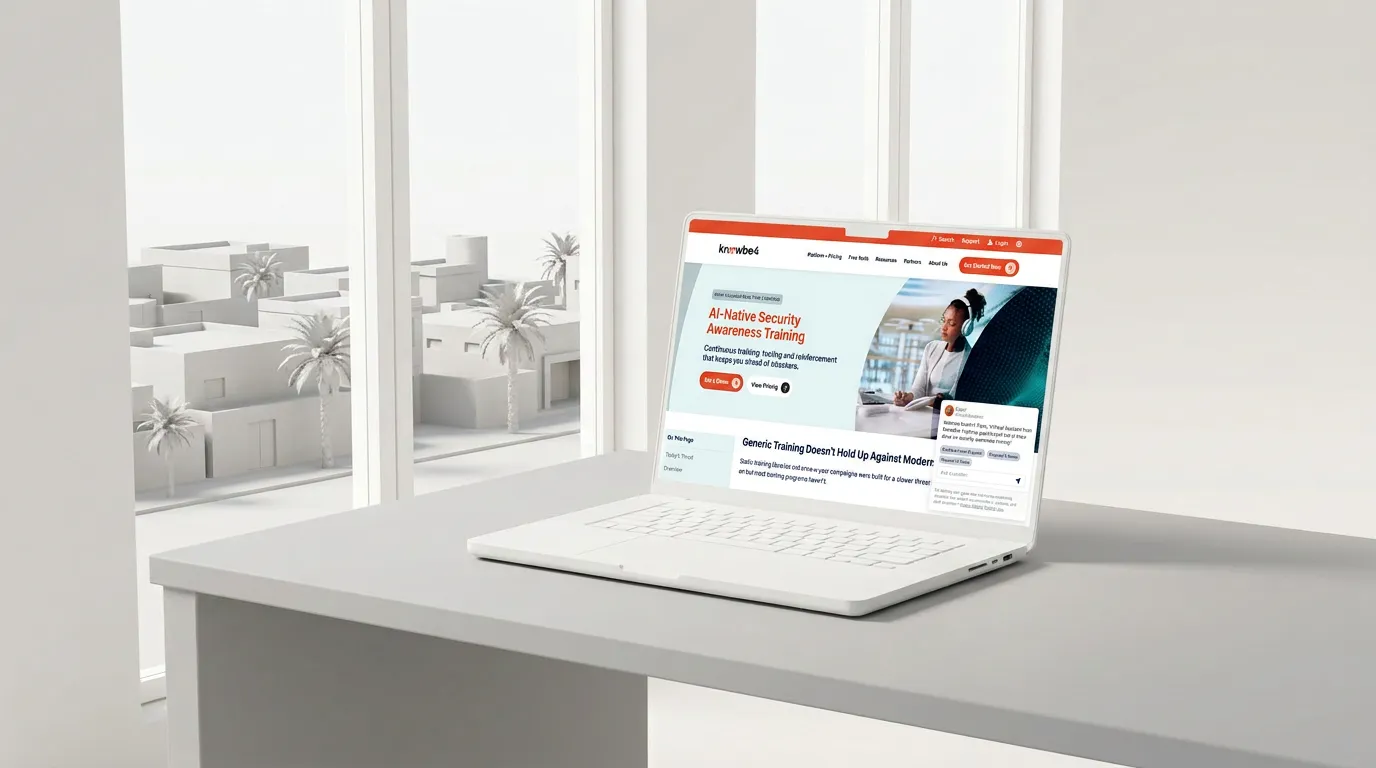
KnowBe4, the world's largest security awareness training platform, provides a structured, data-driven defense against these threats. As the official KnowBe4 distributor in Saudi Arabia, Blue Edge for Communication and Technology (BEC) delivers this platform directly to organizations seeking to transform their employees from security vulnerabilities into their strongest line of defense.
What Makes Phishing So Effective Against Saudi Organizations?
Phishing succeeds not because of technical weakness—it succeeds because of human behavior. Attackers exploit urgency, authority, and familiarity to manipulate employees into clicking malicious links or surrendering credentials.
Several factors amplify phishing risk in the Saudi context:
- Rapid workforce digitization across government and private sectors has outpaced security awareness programs
- Multilingual environments (Arabic and English) create opportunities for attackers to craft highly targeted, language-specific lures
- High email volume in corporate environments makes it easier for phishing attempts to blend into legitimate communications
- Limited security training in many organizations leaves employees without the skills to identify red flags
The result: even well-resourced organizations remain exposed, not because their firewalls failed, but because an employee clicked a link.
How KnowBe4 Works: A Platform Built for Human Risk Management
KnowBe4 approaches cybersecurity from a unique angle—it treats human behavior as a measurable, manageable risk. The platform operates across three core pillars:
1. Simulated Phishing Campaigns
KnowBe4 enables security teams to send realistic, controlled phishing simulations to employees. These tests mirror real-world attack techniques and identify who clicked, who reported, and who remains vulnerable. The platform offers thousands of customizable templates—including Arabic-language scenarios relevant to Saudi users.
2. Automated Security Awareness Training
Employees who fail phishing simulations are automatically enrolled in targeted training modules. These are short, engaging, and designed to change behavior—not just tick a compliance box. Content covers phishing, ransomware, social engineering, and more.
3. Risk Scoring and Reporting
KnowBe4's dashboard provides a clear Phish-prone Percentage (PPP)—a real-time metric showing the proportion of employees likely to fall for a phishing attack. Leadership teams receive actionable insights, not just data, enabling informed decisions on training investment and policy.
KnowBe4 vs. Traditional Security Awareness Methods
| Feature | Traditional Training | KnowBe4 Platform |
|---|---|---|
| Training format | Annual classroom sessions | Continuous, automated modules |
| Phishing simulation | Rarely conducted | Ongoing, customizable campaigns |
| Risk measurement | Difficult to quantify | Real-time Phish-prone Percentage |
| Language support | Limited | Arabic and English templates available |
| Compliance alignment | Manual tracking | NCA-aligned reporting tools |
| Employee engagement | Low (passive) | High (interactive, gamified) |
Traditional awareness programs deliver information once and hope it sticks. KnowBe4 builds lasting behavioral change through repetition, measurement, and targeted intervention.
Case Study: A Saudi Financial Services Firm Reduces Phishing Risk by 73%
A mid-sized financial services company based in Riyadh—operating with approximately 400 employees across three regional offices—faced a growing phishing problem. Over a 12-month period, the organization's IT team recorded multiple credential-compromise incidents, two of which escalated to unauthorized system access.
The challenge: Employees had received basic cybersecurity training during onboarding, but no structured ongoing awareness program existed. Leadership lacked visibility into which departments carried the highest human risk.
The KnowBe4 implementation (via BEC):
- Baseline phishing simulation conducted across all staff
- Initial Phish-prone Percentage recorded at 38%—meaning more than one in three employees was likely to click a malicious link
- Automated training modules deployed based on simulation results
- Monthly phishing simulations introduced, with Arabic-language templates for operations staff
Results after 12 months:
- Phish-prone Percentage dropped to 10.3%—a 73% reduction
- Employee-reported phishing attempts increased by 210%, indicating stronger awareness and confidence
- Zero credential-compromise incidents recorded in the final quarter of the program
- IT team reduced time spent on phishing-related incident response by an estimated 40%
This outcome reflects what consistent, data-driven security awareness training achieves when implemented correctly. The technology provides the framework; behavioral change delivers the result.
Why KnowBe4 Aligns with Saudi Arabia's Cybersecurity Regulatory Framework
The National Cybersecurity Authority (NCA) has issued the Essential Cybersecurity Controls (ECC) as the baseline standard for organizations operating in the Kingdom. Among its requirements, the ECC mandates cybersecurity awareness and training programs for all personnel with access to organizational systems.
KnowBe4 directly supports compliance with these requirements through:
- Documented training completion records for audit purposes
- Phishing simulation reports that demonstrate active risk assessment
- Policy acknowledgment tools that track employee understanding of cybersecurity policies
- Role-based content tailored to different access levels and departments
For regulated sectors—including banking, energy, and government-linked entities—this alignment is not optional. KnowBe4, delivered through a certified local distributor such as BEC, ensures that compliance documentation is as robust as the training itself.
Building a Phishing-Resistant Culture in Your Organization
Technical controls—firewalls, email filters, endpoint protection—are essential. However, no technical control eliminates the human variable. An employee who bypasses a warning prompt or forwards credentials in response to an urgent request undermines every layer of security beneath them.
KnowBe4 shifts this dynamic by making security awareness a continuous organizational habit. The platform's gamification elements, departmental leaderboards, and recognition features turn security training from an obligation into engagement. Over time, employees begin to self-report suspicious emails, ask questions before clicking, and hold one another accountable.
This cultural shift represents the most durable form of anti-phishing defense available to Saudi organizations today.
Frequently Asked Questions
-
What is KnowBe4 and how does it help with anti-phishing in Saudi Arabia?
KnowBe4 is a security awareness training and simulated phishing platform used by organizations worldwide. In Saudi Arabia, it helps businesses reduce phishing risk by training employees to recognize and report phishing attempts through realistic simulations, automated learning modules, and measurable risk reporting.
-
How long does it take to see results from KnowBe4 training?
Most organizations see a measurable reduction in their Phish-prone Percentage within 90 days of deploying KnowBe4. Sustained programs running 12 months or longer typically achieve reductions of 60–80%, based on KnowBe4's published industry benchmarks.
-
Does KnowBe4 support Arabic-language phishing simulations?
Yes. KnowBe4 offers phishing simulation templates and training content in Arabic, making it directly applicable to Saudi workforces operating in bilingual environments.
-
Is KnowBe4 compliant with Saudi Arabia's NCA cybersecurity requirements?
KnowBe4 supports compliance with the NCA's Essential Cybersecurity Controls (ECC) by providing documented training records, phishing simulation reports, and policy acknowledgment tools—all of which are relevant to NCA audit requirements.
-
How can Saudi organizations get started with KnowBe4?
As the official KnowBe4 distributor in Saudi Arabia, Blue Edge for Communication and Technology (BEC) manages the full deployment process—from initial baseline assessment and platform configuration to ongoing support and reporting. Organizations can contact Blue Edge directly to arrange a consultation and platform demonstration.
About Blue Edge
Blue Edge Company is a value-added technology distributor based in Dammam, Saudi Arabia, supplying interactive displays, smart building systems, networking infrastructure and IT security software to businesses and residential projects across the Kingdom, with installation and technical support.
Learn more about Blue Edge →Published 5 July 2026 • Last updated 23 September 2026 • This article is reviewed when standards, regulations or product guidance change.