Shopping Cart

- Articles
- Cybersecurity
- Data Breach Response Checklist for Saudi Businesses
Data Breach Response Checklist for Saudi Businesses
Follow this data breach response checklist to contain cyber incidents, protect sensitive data, meet compliance requirements, and minimize business disruption in Saudi Arabia.
By Blue Edge Team | Published Jul 22, 2026 | Updated Sep 23, 2026 | 5 min read
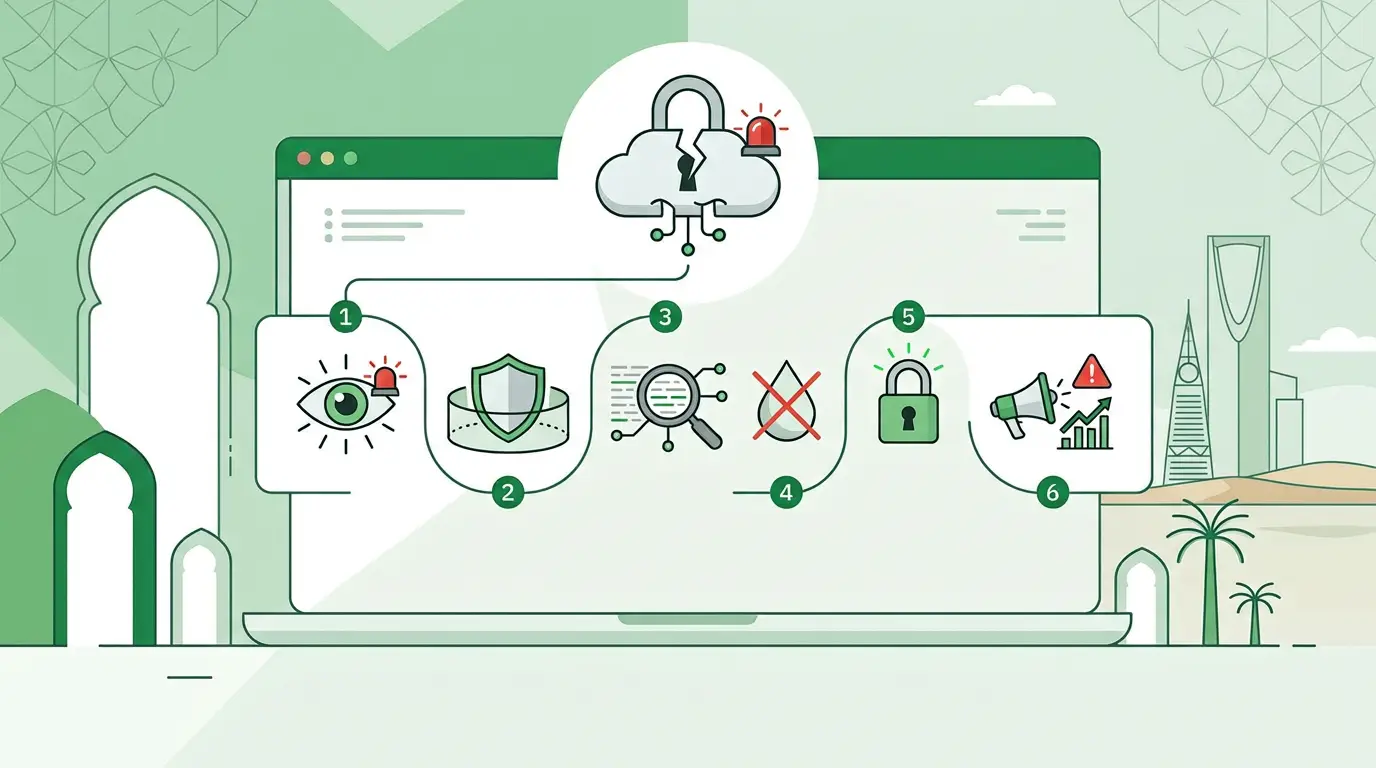
Quick answer
When a data breach occurs, Saudi businesses must act within hours—not days. The response checklist covers containment, legal notification under PDPL, stakeholder communication, forensic investigation, and post-incident review. Following a structured plan significantly reduces financial and reputational damage.
Data breaches are no longer rare events reserved for multinational corporations. Saudi businesses of all sizes are increasingly targeted, and the consequences of a slow or poorly managed response can be severe—regulatory penalties, reputational damage, and lasting loss of customer trust.
Saudi Arabia's Personal Data Protection Law (PDPL), enforced by the National Data Management Office (NDMO), sets clear obligations for how organizations must handle breaches. Understanding those obligations—and having a rehearsed checklist ready before an incident occurs—is the difference between a managed crisis and an uncontrolled one.
This guide walks through the exact steps Saudi businesses should take when a breach is detected, from the first 24 hours to long-term remediation.
Step 1: Contain the Breach Immediately (0–4 Hours)
Speed is critical. The moment a breach is suspected, the priority is to stop further data exposure.
Immediate actions:
- Isolate affected systems from the network to prevent lateral movement by attackers
- Revoke compromised credentials and reset access for impacted accounts
- Preserve system logs and forensic evidence—do not wipe or restart affected devices prematurely
- Activate your incident response team (IRT), including IT security, legal, and executive leadership
Assign a dedicated incident commander to coordinate all response activities. Unclear ownership during the first hours is one of the most common reasons breaches escalate unnecessarily.
Step 2: Assess the Scope and Severity (4–12 Hours)
Once the breach is contained, conduct a rapid assessment to understand what was compromised and how.
Key assessment questions:
- What data was accessed or exfiltrated? (personal data, financial records, intellectual property)
- How many individuals or entities are affected?
- Was the breach caused by an external attack, insider threat, or system misconfiguration?
- Is the vulnerability still active, or has it been fully closed?
Document every finding in a breach incident log. This record will be essential for regulatory reporting and any subsequent legal proceedings.
Step 3: Report to Authorities Under PDPL (Within 72 Hours)
Saudi Arabia's PDPL requires organizations to notify the NDMO of breaches involving personal data within 72 hours of becoming aware of the incident. Failing to meet this deadline can result in regulatory fines.
Notification must include:
- Nature of the breach and the type of data involved
- Number of individuals affected
- Likely consequences of the breach
- Measures taken or planned to address the breach
If notifying all affected individuals is not feasible immediately, a public communication may be required. Consult your legal team to confirm the specific obligations that apply to your organization's data classification and sector.
Step 4: Notify Affected Individuals and Stakeholders
Transparency builds trust—especially in a crisis. Affected individuals have the right to know that their data has been compromised, and timely communication demonstrates organizational accountability.
Communication best practices:
- Use clear, plain language—avoid technical jargon
- Specify what data was exposed and what the individual should do (e.g., change passwords, monitor accounts)
- Provide a dedicated contact point for questions
- Avoid speculative statements about the cause before the investigation is complete
Internally, brief senior leadership, the board, and relevant department heads. If the breach affects third-party partners or vendors, notify them through established data processing agreements.
Step 5: Conduct a Full Forensic Investigation
Once immediate containment and notifications are handled, commission a thorough forensic investigation—either through your internal security team or an accredited third-party cybersecurity firm.
The investigation should determine:
- The initial attack vector (phishing, vulnerability exploitation, credential theft, etc.)
- The timeline of the breach from entry to detection
- Whether any data was exfiltrated or only accessed
- The full list of systems and data repositories affected
The forensic report will inform your remediation plan and may be required by regulators or insurers.
Breach Response Timeline: At a Glance
| Timeframe | Action |
|---|---|
| 0–4 hours | Contain breach, activate IRT, preserve evidence |
| 4–12 hours | Assess scope, classify affected data |
| 12–24 hours | Begin legal review, prepare regulatory notification |
| Within 72 hours | Notify NDMO as required under PDPL |
| 1–2 weeks | Notify affected individuals, complete forensic review |
| 1–3 months | Remediate vulnerabilities, update policies and controls |
Step 6: Remediate Vulnerabilities and Strengthen Controls
A breach is also an audit. Once the investigation is complete, use the findings to systematically close security gaps.
Remediation priorities:
- Patch or reconfigure the specific vulnerability exploited
- Implement or strengthen multi-factor authentication (MFA) across all systems
- Review and tighten access controls using the principle of least privilege
- Update endpoint detection and response (EDR) tools
- Conduct mandatory security awareness training for all staff
For Saudi businesses operating under Vision 2030's digital transformation agenda, cybersecurity resilience is a competitive requirement—not just a compliance obligation.
Step 7: Conduct a Post-Incident Review
Within 30 days of resolving the breach, conduct a structured post-incident review with all relevant stakeholders.
The review should cover:
- What worked in the response and what did not
- Whether the incident response plan performed as expected
- Gaps in detection, communication, or containment
- Updates required to policies, procedures, and training programs
Document the outcomes and assign clear ownership for each corrective action. Schedule a follow-up review at 90 days to confirm implementation.
Building a Resilient Breach Response Culture in Saudi Arabia
Responding to a data breach effectively requires more than a checklist—it requires preparation, practiced protocols, and a culture that treats cybersecurity as a business priority.
Saudi businesses should conduct tabletop breach simulations at least once a year, ensure their incident response plan is reviewed regularly against PDPL updates, and maintain relationships with certified cybersecurity partners before an incident occurs.
The organizations that recover fastest from breaches are those that prepared when everything was calm—not those scrambling to build a plan under pressure.
Take action now: Review your current incident response plan against the checklist above, and identify any gaps before a breach forces your hand.
Frequently Asked Questions
-
What does Saudi Arabia's PDPL require when a data breach occurs?
Under Saudi Arabia's Personal Data Protection Law (PDPL), organizations must notify the National Data Management Office (NDMO) within 72 hours of becoming aware of a personal data breach. The notification must include the nature of the breach, the type and volume of data affected, likely consequences, and the measures being taken to address it.
-
What is the first thing a Saudi business should do after detecting a data breach?
The immediate priority is containment—isolating affected systems, revoking compromised credentials, and preserving forensic evidence. An incident response team should be activated within the first four hours to coordinate the response and prevent further data exposure.
-
How long does a data breach investigation typically take?
A forensic investigation typically takes between one and four weeks, depending on the complexity of the breach and the scale of systems affected. More sophisticated attacks, such as advanced persistent threats (APTs), may require longer investigation periods. Using a certified third-party cybersecurity firm can accelerate the process.
-
Do small businesses in Saudi Arabia need a formal incident response plan?
Yes. Saudi Arabia's PDPL applies to any organization that collects or processes personal data, regardless of size. Small businesses are equally exposed to regulatory penalties and reputational harm. A documented incident response plan—even a simplified one—significantly improves response speed and reduces post-breach damage.
-
What are the penalties for failing to report a data breach in Saudi Arabia?
The PDPL empowers the NDMO to impose fines for non-compliance, including failure to report breaches within the required timeframe. Penalties can include significant financial fines and, in cases of gross negligence, further regulatory action. Exact fine amounts depend on the nature and severity of the violation.
About Blue Edge
Blue Edge Company is a value-added technology distributor based in Dammam, Saudi Arabia, supplying interactive displays, smart building systems, networking infrastructure and IT security software to businesses and residential projects across the Kingdom, with installation and technical support.
Learn more about Blue Edge →Published 22 July 2026 • Last updated 23 September 2026 • This article is reviewed when standards, regulations or product guidance change.