Shopping Cart

- Articles
- Cybersecurity
- Supply Chain Attacks: The Hidden Risk in Your Vendor Network
Supply Chain Attacks: The Hidden Risk in Your Vendor Network
Learn how supply chain attacks exploit trusted vendors, software providers, and third-party partners, and discover proven strategies to reduce vendor risk and strengthen enterprise cybersecurity. Modern attacks increasingly target trusted relationships rather than organizations directly.
By Blue Edge Team | Published Aug 17, 2026 | Updated Sep 23, 2026 | 6 min read
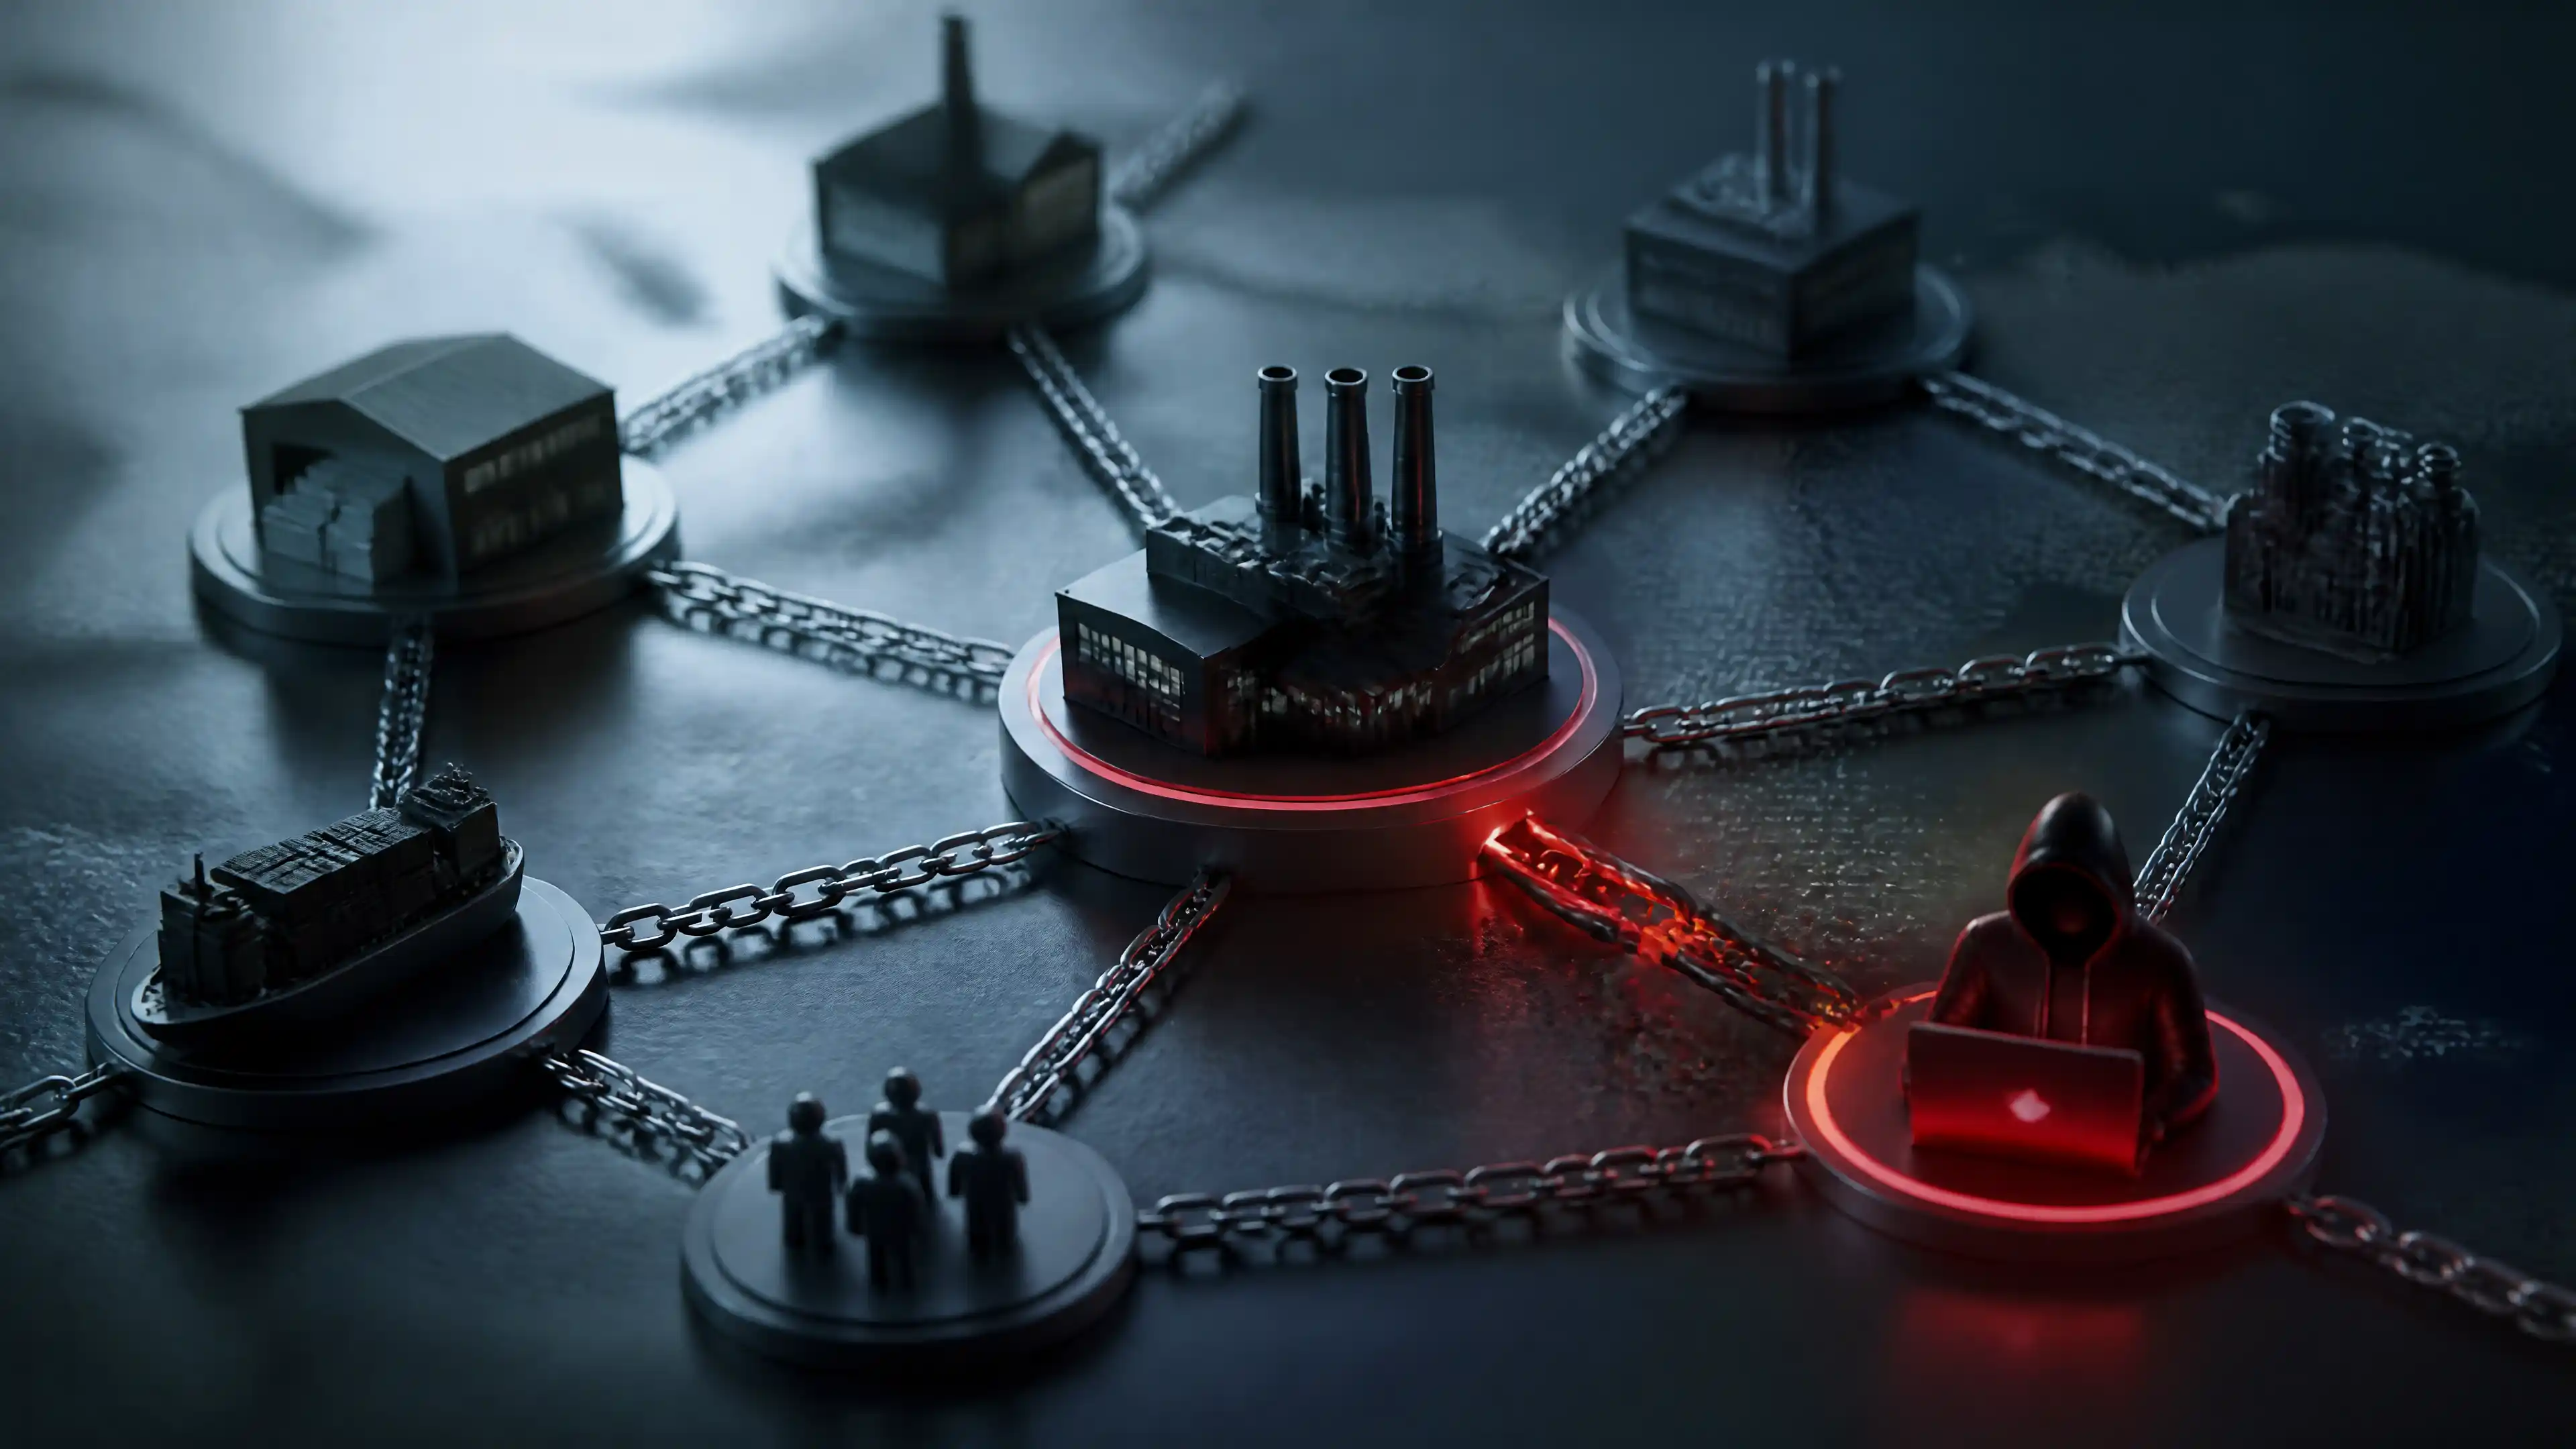
Supply chain attacks occur when cybercriminals compromise a trusted third-party vendor to infiltrate a target organization. These attacks are difficult to detect because they exploit established trust relationships. Organizations must vet vendors rigorously, monitor third-party access continuously, and implement zero-trust security frameworks to reduce exposure.
Your perimeter defenses are only as strong as the weakest vendor in your network. Firewalls, endpoint protection, and internal security policies protect what you control—but what about the software providers, IT consultants, and cloud platforms you trust implicitly?
Supply chain attacks have surged in both frequency and sophistication over the past decade. The SolarWinds breach of 2020 exposed approximately 18,000 organizations—including multiple U.S. federal agencies—through a single compromised software update. The message was stark: attackers no longer need to break down your front door when a trusted vendor will open it for them.
This post breaks down exactly how supply chain attacks work, what makes them so dangerous, and the practical steps your organization can take to close the gap.
What Is a Supply Chain Attack—and Why Is It So Hard to Detect?
A supply chain attack targets a vendor, supplier, or software provider that has privileged access to your systems. Rather than attacking your organization directly, threat actors compromise an upstream partner and use that foothold to reach their actual target.
The reason these attacks are so effective is simple: they exploit trust. When a vendor's software update arrives in your environment, your security tools typically treat it as legitimate. There are no phishing emails to flag, no unusual login attempts to block. The malicious code arrives wearing a trusted badge.
Detection is further complicated by the time gap between infection and discovery. According to IBM's Cost of a Data Breach Report (2023), the average breach takes 204 days to identify. In supply chain scenarios, that window is often wider—attackers frequently establish persistence before triggering any visible activity.
How Supply Chain Attacks Work: The Attack Lifecycle
Understanding the mechanics helps organizations identify where to intervene. A typical supply chain attack progresses through the following stages:
- Vendor compromise — Attackers identify and infiltrate a supplier with access to the target's environment. This may involve credential theft, exploiting unpatched vulnerabilities, or inserting malicious code into a software build pipeline.
- Payload delivery — The compromised vendor delivers the malicious payload—often through a software update, a shared file, or a remote access tool—directly into the target's network.
- Lateral movement — Once inside, attackers move laterally across systems, escalating privileges and establishing persistent access points.
- Data exfiltration or disruption — The final stage varies by motive: financial theft, intellectual property exfiltration, ransomware deployment, or long-term espionage.
Common Supply Chain Attack Vectors
| Attack Vector | Description | Notable Example |
|---|---|---|
| Software updates | Malicious code inserted into legitimate software updates | SolarWinds Orion (2020) |
| Open-source dependencies | Compromised packages in public repositories (e.g., npm, PyPI) | Event-stream npm attack (2018) |
| Third-party IT providers | Attackers pivot through managed service providers (MSPs) | Kaseya VSA ransomware attack (2021) |
| Hardware tampering | Malicious firmware or components inserted during manufacturing | Bloomberg "The Big Hack" (alleged, 2018) |
| Cloud and SaaS integrations | Exploiting OAuth tokens or API keys shared with third-party platforms | Okta breach via Sitel (2022) |
Each vector presents unique challenges. Software-based attacks are by far the most prevalent, accounting for the majority of high-profile incidents in recent years.
Comparing Your Defense Options: What Actually Works?
Not all security measures provide equal protection against supply chain threats. The table below compares common approaches by effectiveness, implementation complexity, and cost.
| Security Measure | Effectiveness Against Supply Chain Attacks | Complexity | Relative Cost |
|---|---|---|---|
| Zero-trust architecture | High — limits lateral movement even after compromise | High | High |
| Vendor risk assessments | Medium-High — identifies risk before onboarding | Medium | Medium |
| Software bill of materials (SBOM) | High — provides full visibility into software components | Medium | Medium |
| Continuous third-party monitoring | High — detects anomalous vendor behavior in real time | High | High |
| MFA for all vendor access | Medium — reduces credential-based compromise | Low | Low |
| Endpoint detection & response (EDR) | Medium — can identify post-compromise behavior | Medium | Medium |
Zero-trust architecture and continuous monitoring offer the strongest defense posture, but they require meaningful investment. For organizations with limited budgets, starting with vendor risk assessments and enforcing MFA across all third-party access points delivers measurable risk reduction at lower cost.
5 Actionable Steps to Reduce Your Supply Chain Risk
1. Build a Vendor Inventory and Risk Tier System
You cannot protect what you haven't mapped. Document every third-party vendor with access to your systems, data, or infrastructure. Categorize vendors by access level and business criticality, then apply proportional scrutiny. High-tier vendors—those with privileged access—warrant the most rigorous review.
2. Require Software Bills of Materials (SBOMs)
An SBOM is a formal inventory of all components within a software product, including open-source libraries and their versions. Requiring SBOMs from your software vendors allows your security team to identify known vulnerabilities within the products you use—before they are exploited.
3. Implement Zero-Trust Access Controls
Operate on the principle that no user or system—internal or external—should be trusted by default. Grant vendors the minimum access required to perform their function, enforce strict authentication, and review access permissions regularly. Zero-trust limits the blast radius when a vendor account is compromised.
4. Monitor Third-Party Activity Continuously
Static, point-in-time assessments are insufficient. Deploy solutions that provide continuous visibility into how vendors are accessing your systems. Behavioral analytics can flag anomalous activity—such as unusual data transfers or off-hours access—before damage is done.
5. Establish a Vendor Incident Response Protocol
Define clearly what happens when a vendor reports a breach, or when you detect suspicious activity originating from a third-party connection. This includes predefined escalation paths, contract clauses requiring breach notification, and the ability to rapidly revoke vendor access if needed.
What Does a Supply Chain Attack Cost Organizations?
The financial consequences are significant and multidimensional. According to IBM's Cost of a Data Breach Report (2023), the average cost of a data breach reached $4.45 million—the highest figure recorded in the report's 18-year history. Breaches involving third parties consistently trend above this average due to the complexity of detection and remediation.
Beyond direct financial losses, organizations face regulatory penalties, reputational damage, and erosion of customer trust—costs that are harder to quantify but equally consequential.
Strengthening Your Vendor Network Starts Now
Supply chain attacks succeed because they exploit the trust your organization has carefully extended to its partners. Closing that gap requires a shift in mindset: every third-party relationship is a potential attack surface, and managing it is not optional.
The good news is that a structured approach—combining vendor risk management, zero-trust principles, continuous monitoring, and clear incident response plans—significantly reduces your exposure. Organizations that treat supply chain security as a core discipline, rather than an afterthought, are far better positioned to detect threats early and contain damage effectively.
If your organization has not yet conducted a thorough third-party risk assessment, now is the time to start. Contact our security team today to learn how we can help you map your vendor ecosystem and implement a defense strategy built for the threats you actually face.
Frequently Asked Questions
-
What is the difference between a supply chain attack and a traditional cyberattack?
A traditional cyberattack targets an organization directly—through phishing, brute force, or exploiting known vulnerabilities. A supply chain attack takes an indirect route, compromising a trusted vendor or supplier to gain access to the intended target. This indirect approach makes supply chain attacks significantly harder to detect and defend against.
-
Which industries are most at risk from supply chain attacks?
All industries that rely on third-party software, cloud services, or managed IT providers carry risk. However, sectors handling sensitive data—including government, financial services, healthcare, and critical infrastructure—are disproportionately targeted due to the value of the data they hold and the complexity of their vendor ecosystems.
-
How can small and mid-sized businesses protect themselves from supply chain attacks?
Smaller organizations should prioritize the following: enforcing MFA across all vendor accounts, maintaining an up-to-date inventory of third-party software, reviewing vendor contracts for security and breach notification clauses, and opting for software from providers that publish SBOMs. These steps deliver meaningful risk reduction without requiring enterprise-level security budgets.
-
What is a Software Bill of Materials (SBOM), and why does it matter?
An SBOM is a structured inventory of every component within a software product, including third-party libraries, open-source packages, and their version numbers. SBOMs enable organizations to quickly identify whether any component within software they use is affected by a newly disclosed vulnerability—reducing the window between vulnerability disclosure and remediation.
-
How quickly can a supply chain attack spread through an organization's network?
Once a supply chain attack delivers its payload, lateral movement can begin within hours. In the SolarWinds breach, attackers had undetected access to victim networks for months before discovery. The speed and scale of propagation depend on the attacker's objectives, the breadth of the vendor's access, and the strength of the victim organization's internal segmentation controls.
About Blue Edge
Blue Edge Company is a value-added technology distributor based in Dammam, Saudi Arabia, supplying interactive displays, smart building systems, networking infrastructure and IT security software to businesses and residential projects across the Kingdom, with installation and technical support.
Learn more about Blue Edge →Published 17 August 2026 • Last updated 23 September 2026 • This article is reviewed when standards, regulations or product guidance change.