Shopping Cart

- Articles
- Networking
- NAT Explained: How It Shields and Scales Your Network
NAT Explained: How It Shields and Scales Your Network
Learn how Network Address Translation (NAT) improves network security, conserves IP addresses, enables internet connectivity, and supports scalable enterprise network infrastructure.
By Blue Edge Team | Published Aug 06, 2026 | Updated Sep 23, 2026 | 8 min read
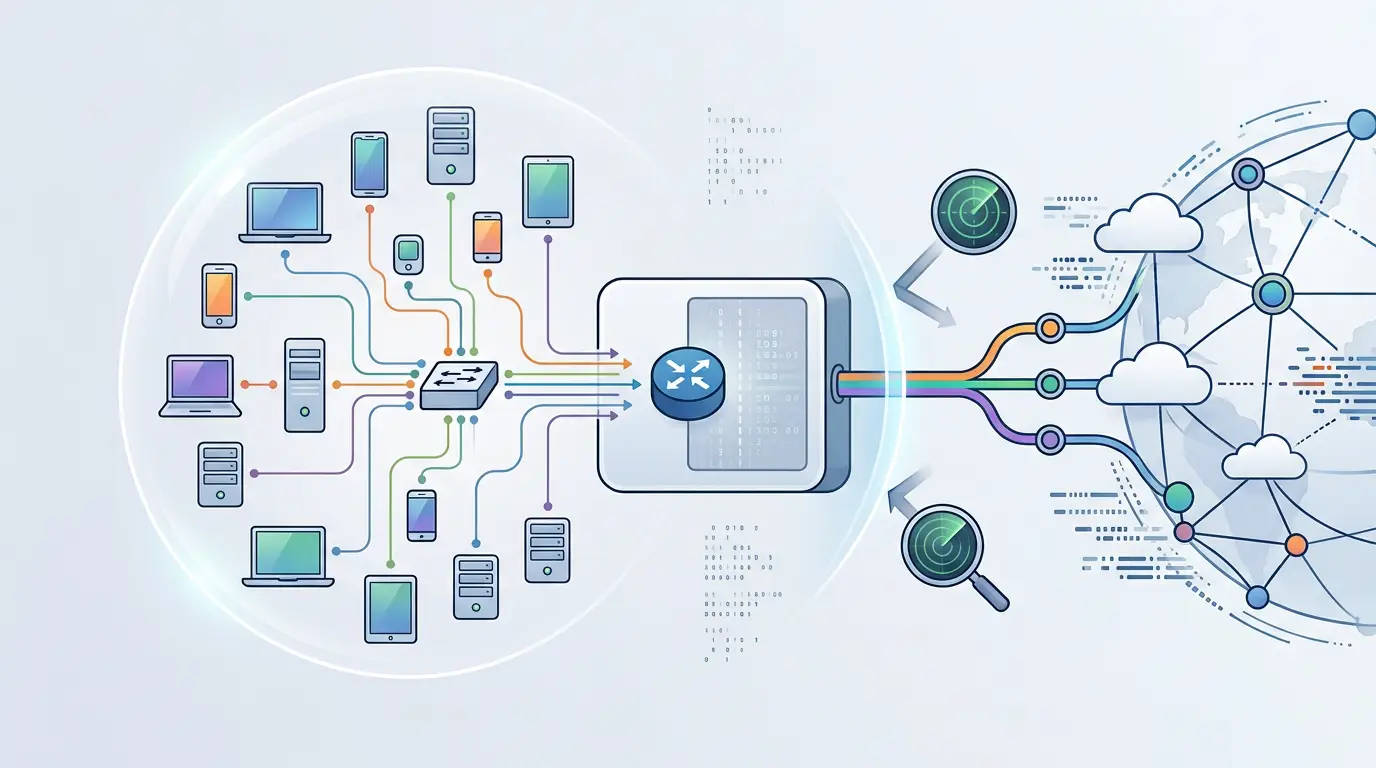
Network Address Translation (NAT) is a method used by routers to map private IP addresses to a single public IP address, enabling multiple devices to share one internet connection while adding a layer of security. NAT is foundational to modern networking—from home routers to enterprise infrastructure.
Every device connected to the internet needs an IP address. Yet the world ran out of available IPv4 addresses years ago. So how does your office of 200 employees—each with a laptop, phone, and tablet—connect to the internet using just one address assigned by your ISP?
The answer is NAT: Network Address Translation.
NAT is one of the most widely deployed networking technologies in existence, yet it operates almost entirely out of sight. It sits inside your router, quietly managing traffic between your internal devices and the outside world. Understanding how NAT works—and why it matters—is essential for anyone responsible for network design, security, or performance.
This guide breaks down NAT from the ground up: what it is, how different types compare, where it protects you, and where its limitations begin.
What Is Network Address Translation (NAT)?
Network Address Translation is a process performed by a router or firewall that modifies the IP address information in packet headers as traffic passes through. At its core, NAT allows devices on a private network—using private IP addresses—to communicate with external networks using one or more public IP addresses.
Private IP address ranges (as defined by RFC 1918) include:
- 10.0.0.0 – 10.255.255.255
- 172.16.0.0 – 172.31.255.255
- 192.168.0.0 – 192.168.255.255
These addresses are not routable on the public internet. NAT acts as the translator, converting private addresses into routable public ones before packets leave your network—and reversing that process when responses arrive.
Why Was NAT Developed?
NAT emerged in the early 1990s as IPv4 address exhaustion became a pressing concern. The IPv4 protocol supports approximately 4.3 billion unique addresses—a number that seemed sufficient in 1981 but proved inadequate as the internet expanded globally.
Rather than immediately transitioning to a new protocol (which eventually became IPv6), NAT offered a pragmatic short-term solution: let many devices share a single public IP address. That "short-term" solution has now been in use for over three decades and remains deeply embedded in global networking infrastructure.
How Does NAT Work? A Step-by-Step Breakdown
When a device on your internal network—say, a laptop with the private IP address 192.168.1.10—sends a request to an external web server, the following occurs:
- The laptop generates a packet with a source IP of 192.168.1.10 and a destination IP of the web server.
- The packet reaches the router, which is running NAT.
- The router replaces the source IP (192.168.1.10) with its own public IP address (e.g., 203.0.113.5) and logs this translation in a NAT table.
- The packet is forwarded to the web server using the public IP.
- The server responds to 203.0.113.5.
- The router receives the response, checks its NAT table, and forwards the packet back to 192.168.1.10.
This entire process happens in milliseconds, and the end user never notices it.
The Three Main Types of NAT
Not all NAT implementations work the same way. Each type serves different use cases and carries distinct trade-offs.
Static NAT
Static NAT maps a single private IP address to a single public IP address—permanently. This one-to-one relationship is typically used for servers that must be consistently reachable from the internet, such as a web server or mail server hosted on-premises.
Dynamic NAT
Dynamic NAT maps private IP addresses to a pool of public IP addresses. The router assigns a public IP from the pool on a first-come, first-served basis. Unlike static NAT, these mappings are temporary and change over time.
PAT (Port Address Translation) — Also Known as NAT Overload
PAT is the most common form of NAT in use today. It maps multiple private IP addresses to a single public IP address by differentiating connections using unique port numbers. This is what your home router does. Hundreds of internal devices can share one public IP address because each connection is tracked by a unique source port number.
NAT Types Compared: Feature Comparison Table
| Feature | Static NAT | Dynamic NAT | PAT (NAT Overload) |
|---|---|---|---|
| IP Mapping | One-to-one | Many-to-pool | Many-to-one |
| Public IPs Required | One per device | One per active session | One for all devices |
| Address Conservation | Low | Moderate | High |
| Inbound Accessibility | Yes (predictable) | Limited | No (by default) |
| Typical Use Case | Hosted servers | Mid-size networks | Home & enterprise routing |
| Session Persistence | Permanent | Temporary | Temporary |
| Configuration Complexity | Low | Moderate | Low to moderate |
| Security Level | Moderate | Moderate | High (hides internal IPs) |
How NAT Protects Your Network
NAT is not a firewall—but it does provide meaningful security benefits as a byproduct of its design.
NAT Conceals Internal Network Structure
Because internal IP addresses are never exposed in outbound traffic, external parties cannot directly observe your network topology. Attackers cannot easily target internal devices without first knowing their private addresses.
NAT Blocks Unsolicited Inbound Connections
By default, PAT only forwards inbound traffic that corresponds to an existing entry in the NAT table—meaning a session that was initiated from inside the network. Unsolicited connection attempts from external sources are silently dropped. This behavior provides implicit protection against many opportunistic attacks.
NAT Reduces the Attack Surface
Fewer public IP addresses means fewer publicly exposed endpoints. This reduction in exposure limits the number of entry points an attacker can probe.
That said, NAT should be treated as a complementary control—not a replacement for a properly configured firewall, intrusion detection system, or zero-trust architecture.
NAT and IPv6: Is NAT Still Necessary?
IPv6 was designed to solve the address exhaustion problem that gave rise to NAT. With 340 undecillion unique addresses available, every device on earth could have its own globally routable IP address—eliminating the need for address translation.
In a pure IPv6 environment, NAT is technically unnecessary. However, the global transition to IPv6 remains incomplete. As of 2024, approximately 45% of Google users access the internet over IPv6 (according to Google's IPv6 Statistics), meaning IPv4 and NAT remain dominant in most real-world deployments.
For organizations operating dual-stack networks (supporting both IPv4 and IPv6), NAT64 and NAT-PT mechanisms exist to facilitate communication between the two protocols.
Common NAT Limitations and Challenges
NAT solves important problems but introduces its own set of complications.
End-to-End Connectivity: Some applications—particularly peer-to-peer, VoIP, and video conferencing tools—rely on direct device-to-device communication. NAT disrupts this by obscuring the true source IP, requiring workarounds like STUN, TURN, or ICE protocols.
Increased Latency (Marginally): Every packet passing through NAT requires translation, which adds a small processing overhead. In high-throughput environments, this can become measurable.
Logging and Troubleshooting Complexity: When multiple users share a single public IP, correlating a specific external connection back to an internal device requires detailed NAT table logging—something that is not always enabled by default.
Incompatibility with Some Protocols: Protocols that embed IP addresses within their payloads (such as FTP in active mode or IPSec) can break under NAT unless specific ALG (Application Layer Gateway) support is configured.
NAT in Enterprise Environments: Key Considerations
For enterprise network architects, NAT decisions extend beyond simple address conservation. Several strategic considerations apply:
- NAT and VPNs: Combining NAT with site-to-site VPNs requires careful planning to avoid IP overlap between connected networks.
- Port Forwarding: Exposing internal services (e.g., a remote desktop or an application server) requires explicit port forwarding rules—each of which introduces a potential security exposure that must be managed.
- NAT Tables and Scalability: In high-session-count environments, NAT tables can become a resource bottleneck. Enterprise-grade routers and next-generation firewalls are designed to handle millions of concurrent NAT sessions.
- Carrier-Grade NAT (CGNAT): ISPs increasingly deploy CGNAT (also known as Large-Scale NAT), where NAT is applied at the carrier level before traffic even reaches your router. This creates a double-NAT scenario that can complicate direct connectivity and port forwarding.
The Right NAT Strategy Depends on Your Use Case
Choosing the correct NAT approach depends on what your network needs to accomplish.
- Choose Static NAT if you host services that must be consistently reachable from the internet, such as a web server, mail relay, or VoIP gateway.
- Choose Dynamic NAT if you manage a mid-sized network where occasional external access is needed but address requirements fluctuate.
- Choose PAT if your priority is address conservation and your network traffic is primarily outbound-initiated—which describes the majority of enterprise and home environments.
No single NAT type is universally superior. The decision should be driven by your access requirements, security posture, and infrastructure scale.
Strengthening Your Network Starts with Understanding It
NAT is a foundational element of how modern networks function. It conserves address space, adds a layer of implicit security, and enables thousands of devices to operate behind a single public IP address. At the same time, it introduces complexity, limits peer-to-peer connectivity, and requires careful configuration in enterprise contexts.
Understanding NAT—its types, its behaviors, its strengths, and its limitations—equips network administrators and IT decision-makers to design infrastructure that is both efficient and secure. As IPv6 adoption continues and network architectures evolve, NAT will remain a critical concept for anyone building or managing connected systems.
If you are evaluating your organization's network infrastructure and want to ensure your routing, security, and connectivity strategies are properly aligned, consult with a certified network professional who can assess your specific environment.
Frequently Asked Questions
-
What is the difference between NAT and a firewall?
NAT translates IP addresses between private and public networks, while a firewall controls which traffic is permitted or denied based on defined rules. NAT provides implicit inbound filtering as a side effect of address translation, but it does not inspect traffic content or enforce access policies. For comprehensive protection, NAT and a firewall should be deployed together.
-
Can two devices on the same network have the same private IP address?
No. Within a single private network, each device must have a unique private IP address. Duplicate IP addresses on the same network cause address conflicts and communication failures. NAT allows multiple devices across different private networks to use the same private IP ranges, since those addresses are never exposed externally.
-
Does NAT slow down internet speeds?
In most deployments, NAT has a negligible impact on speed. Modern routers handle NAT translation efficiently at hardware level. However, in very high-throughput environments—such as data centers or large enterprise networks processing millions of simultaneous sessions—NAT processing can become a performance consideration that warrants purpose-built hardware.
-
What is double NAT, and is it a problem?
Double NAT occurs when two devices on your network both perform NAT—for example, a modem/router provided by your ISP and a secondary router you've added. Double NAT can cause issues with VPNs, gaming, remote desktop access, and other services that require specific port forwarding. It can be resolved by placing the ISP device in bridge mode or using DMZ settings.
-
Is NAT still relevant with IPv6?
IPv6 eliminates the address scarcity problem that originally necessitated NAT. In a fully IPv6 network, NAT is not required. However, because global IPv6 adoption remains incomplete, NAT continues to be widely deployed in IPv4 and dual-stack environments. Organizations transitioning to IPv6 should plan their NAT strategy carefully during the migration period.
About Blue Edge
Blue Edge Company is a value-added technology distributor based in Dammam, Saudi Arabia, supplying interactive displays, smart building systems, networking infrastructure and IT security software to businesses and residential projects across the Kingdom, with installation and technical support.
Learn more about Blue Edge →Published 6 August 2026 • Last updated 23 September 2026 • This article is reviewed when standards, regulations or product guidance change.